For SaaS companies on AWS · Built in Australia
AWS audit readiness and customer assurance for growing SaaS companies.
Start with a free, read-only scan of your AWS account. See your SOC 2 and ISO/IEC 27001 gaps, fix them, then use the same evidence to answer customer security reviews and to give your auditor an organised package.
Read-only access · Hosted in Australia (AWS Sydney) · No card needed · TrustProof does not certify. Your auditor forms their own opinion.
How it works
From a free scan to an organised audit file.
- STEP 1 · FREE
Run a free, read-only AWS scan
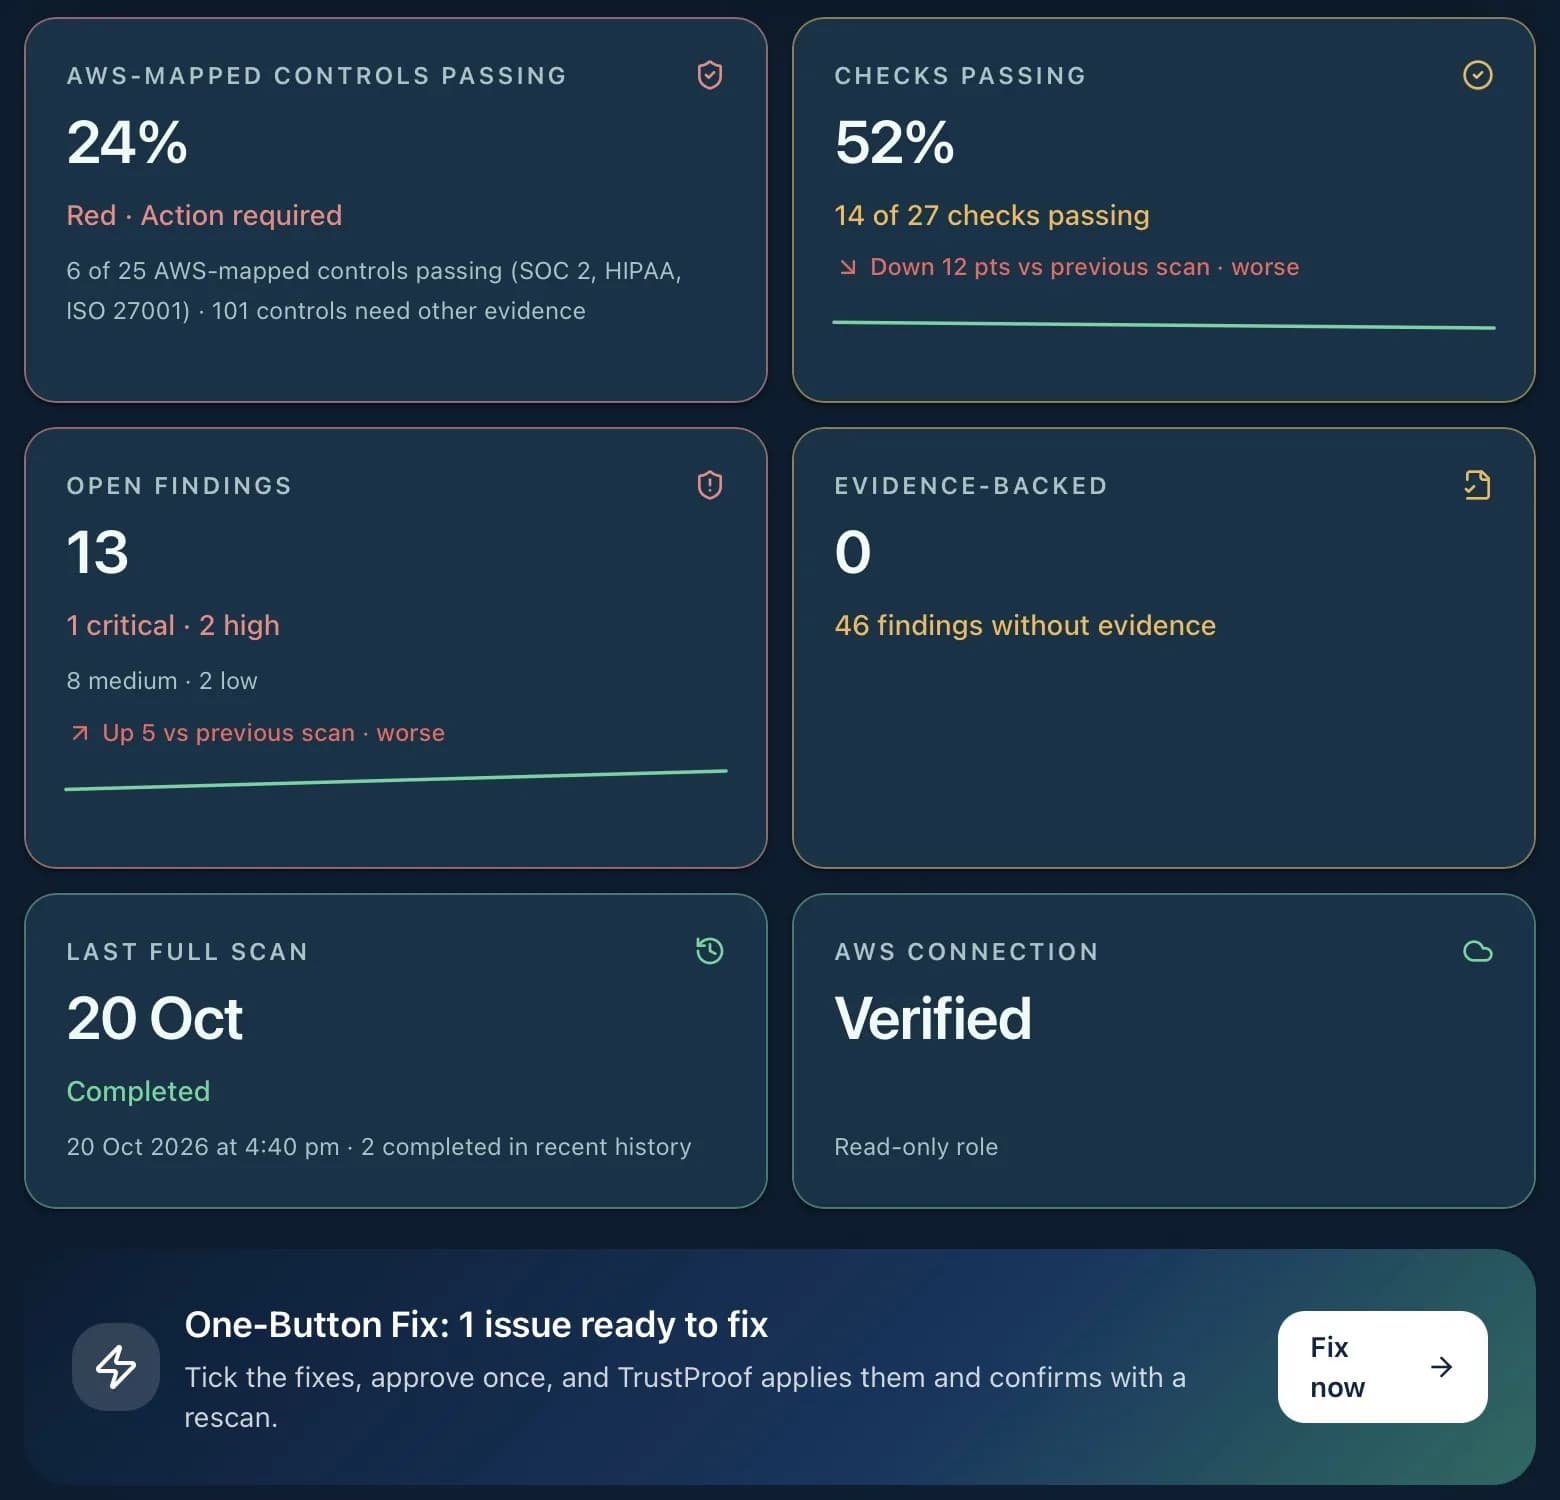
Connect a read-only role you can remove at any time: no passwords, no stored keys. TrustProof runs 46 read-only checks across identity, storage, network, logging and backups. It reads settings, never the data inside your buckets or databases. A scan takes minutes.
Start your free AWS scan →What the scan checks, and what it doesn't →
- STEP 2
See your SOC 2 and ISO/IEC 27001 gaps
Findings are ranked by risk and mapped to selected SOC 2 criteria and ISO/IEC 27001 Annex A controls. Each mapped control shows red, amber or green, so you, your board and your auditor see the same picture.
- STEP 3
Fix them, with your engineer in charge
Every finding comes with plain steps your team can follow. For findings TrustProof supports, One-Button Fix prepares the change and applies it only after your engineer approves it: A$1,499 one-off, inc GST, for one AWS account for 30 days.
- STEP 4
Answer customer security reviews from the same evidence
With the Security Response add-on, answer customer security questionnaires and share a trust portal, drawing on the evidence you have already collected.
- STEP 5Early access
Hand an organised package to your CPA or certification body
Invite your auditor to their own read-only portal. They review the evidence you release, organised by requirement, and form their own opinion.
Built for your CPA and auditor
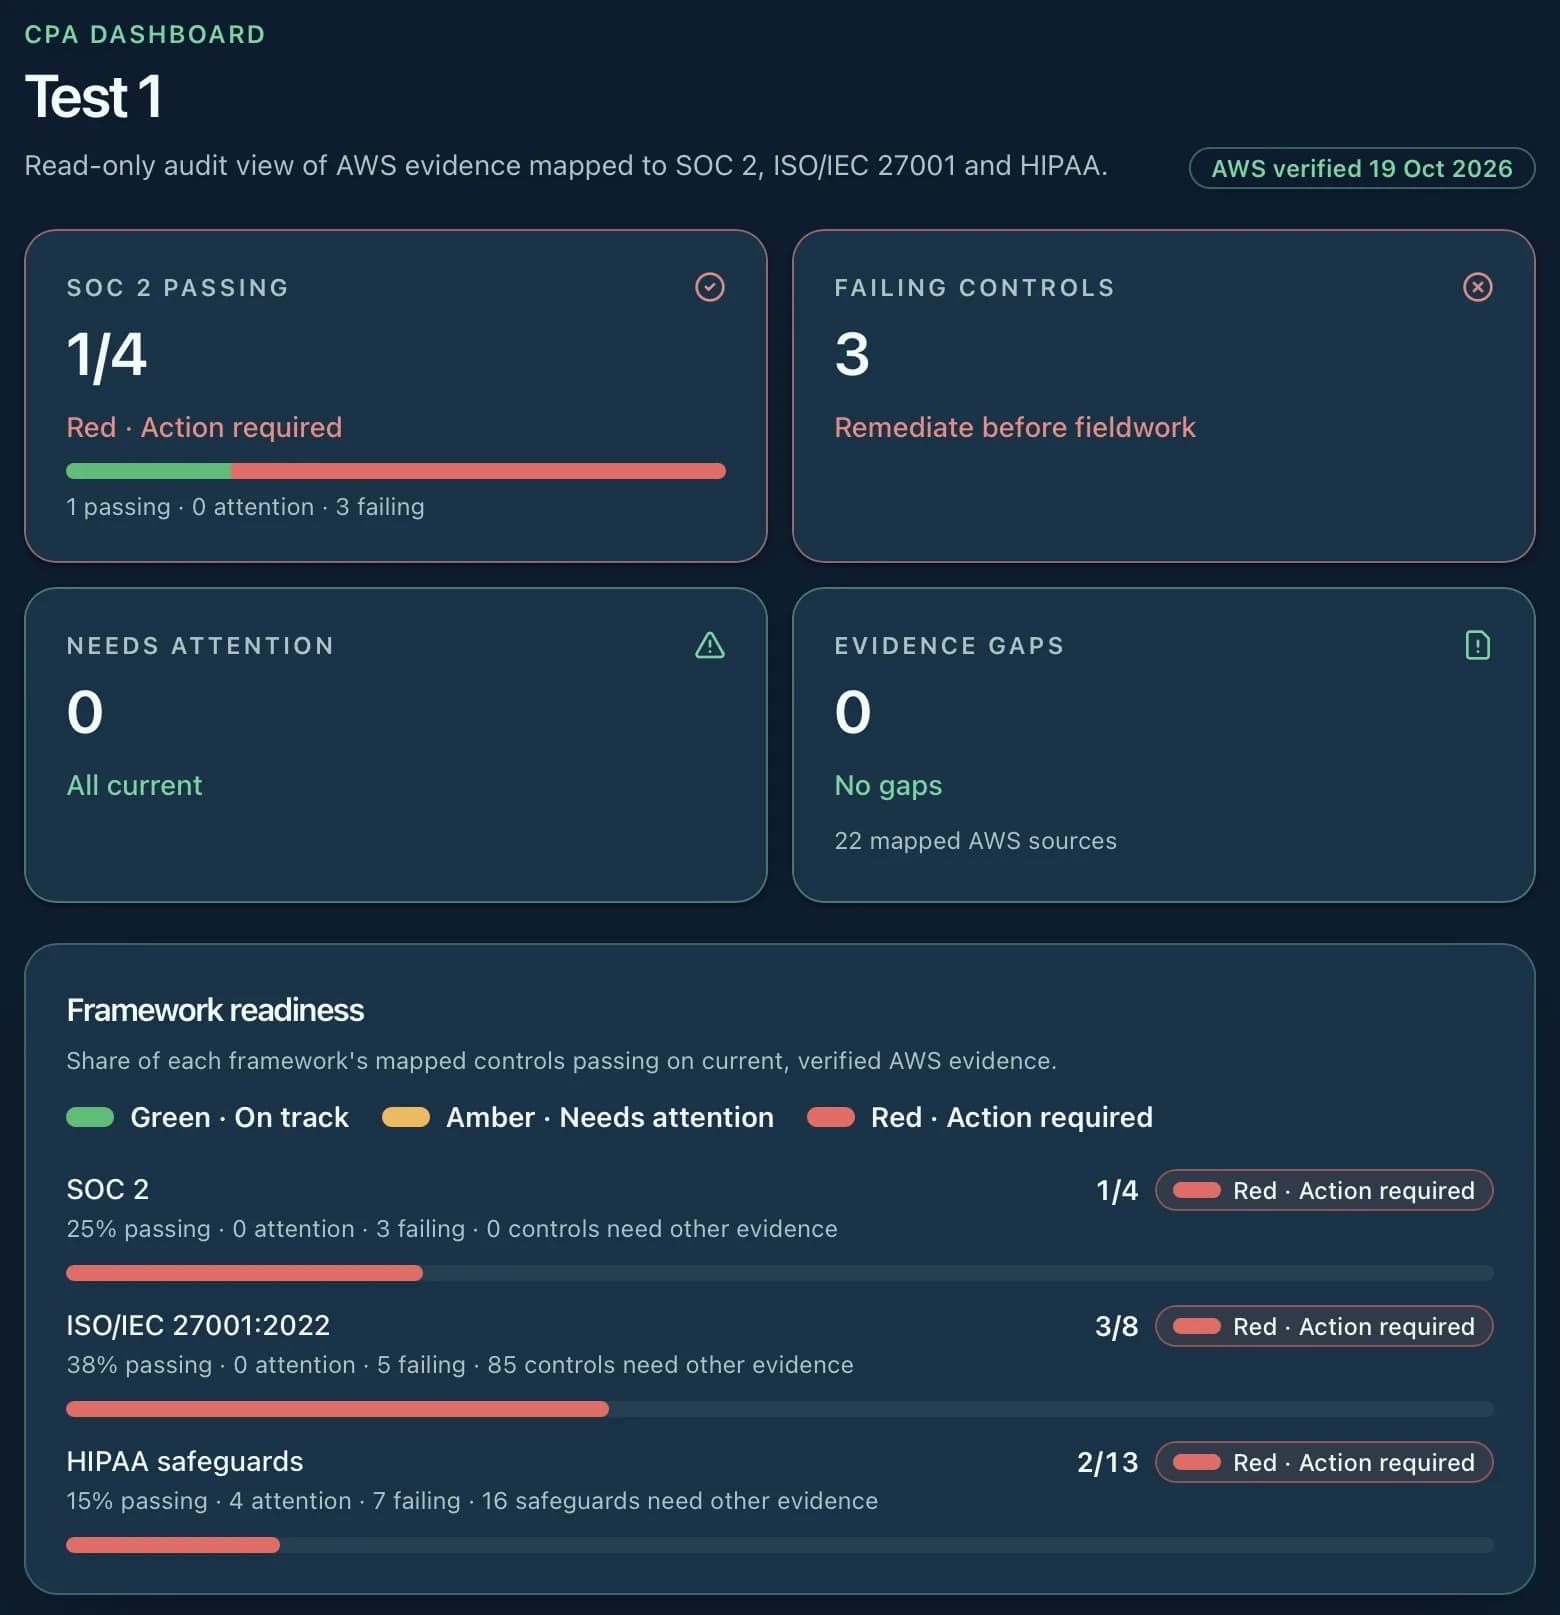
Early accessYour auditor gets their own sign-in and their own dashboard.
Most audits still run on shared folders and email. With TrustProof, you invite your CPA or certification body and they sign in to a dedicated Auditor Dashboard, with two-step verification, to review everything you release. Every client they audit with TrustProof sits in one place.
- Read-only and time-limited: they see only the evidence you release
- Evidence organised by requirement, with AWS check results, versions and owner sign-offs attached
- Owner sign-offs fingerprinted with SHA-256, so approved documents can't change unnoticed
- Requests, answers, views and downloads all logged for the audit file
- Statement of Applicability export for ISO frameworks
For CPA firms and certification bodies
Less chasing when your clients use TrustProof.
No more chasing screenshots. Evidence arrives organised by requirement, with sign-offs, versions and AWS checks attached. Your firm keeps one login for every TrustProof client, and the testing and the opinion stay yours.
- Write-once evidence storage: versions are kept, never overwritten
- A dedicated CPA and Auditor Dashboard, with its own sign-in
- Independence kept: you review, you decide, TrustProof never certifies
Who does what
TrustProof prepares. Your auditor decides.
TrustProof prepares and organises your evidence. Your auditor tests it independently and forms their own opinion, and you remain responsible for your controls.
Read-only by default
The scan role can only read settings. Changes need a separate role you add and an approval you give.
Hosted in Australia
Runs on AWS in Sydney, encrypted at rest and in transit.
Honest about scope
TrustProof helps you prepare for audit. It does not certify, and it never claims to.
Also covers
Need more than SOC 2 or ISO/IEC 27001?
The same account and evidence extend to other frameworks and modules as you grow. Each further framework is an add-on from A$599/month.
Modules
- Risk ManagementAn organisation-wide risk register with owners, treatments and reviews.
- Penetration TestingPlan engagements, track findings and retests, delivered by qualified partner testers.
- Security ResponseAnswer customer security questionnaires and share a trust portal.
- Security AwarenessStaff training and evidence that it happened, built into your dashboard.
- Vendor RiskAssess and monitor the suppliers your business depends on.
- PrivacyPrivacy registers, processing records and retention reviews.
- AI ComplianceA register of your AI systems, risk assessments with sign-off, approved tools and AI incidents.
Pricing
Clear prices in Australian dollars.
The first AWS scan is free. Plans are a one-off Readiness Programme for your first framework plus a monthly or yearly price. All prices include GST.
Growth
A$899/month
+ A$5,999 Readiness Programme
Framework programme and AWS checks
Corporate
A$2,199/month
+ A$21,999 Readiness Programme
Includes Continuous Monitoring
Enterprise
A$4,999/month
+ A$47,999 Readiness Programme
Includes Continuous Monitoring