Frameworks · ISO/IEC 27001
ISO/IEC 27001 readiness for teams on AWS
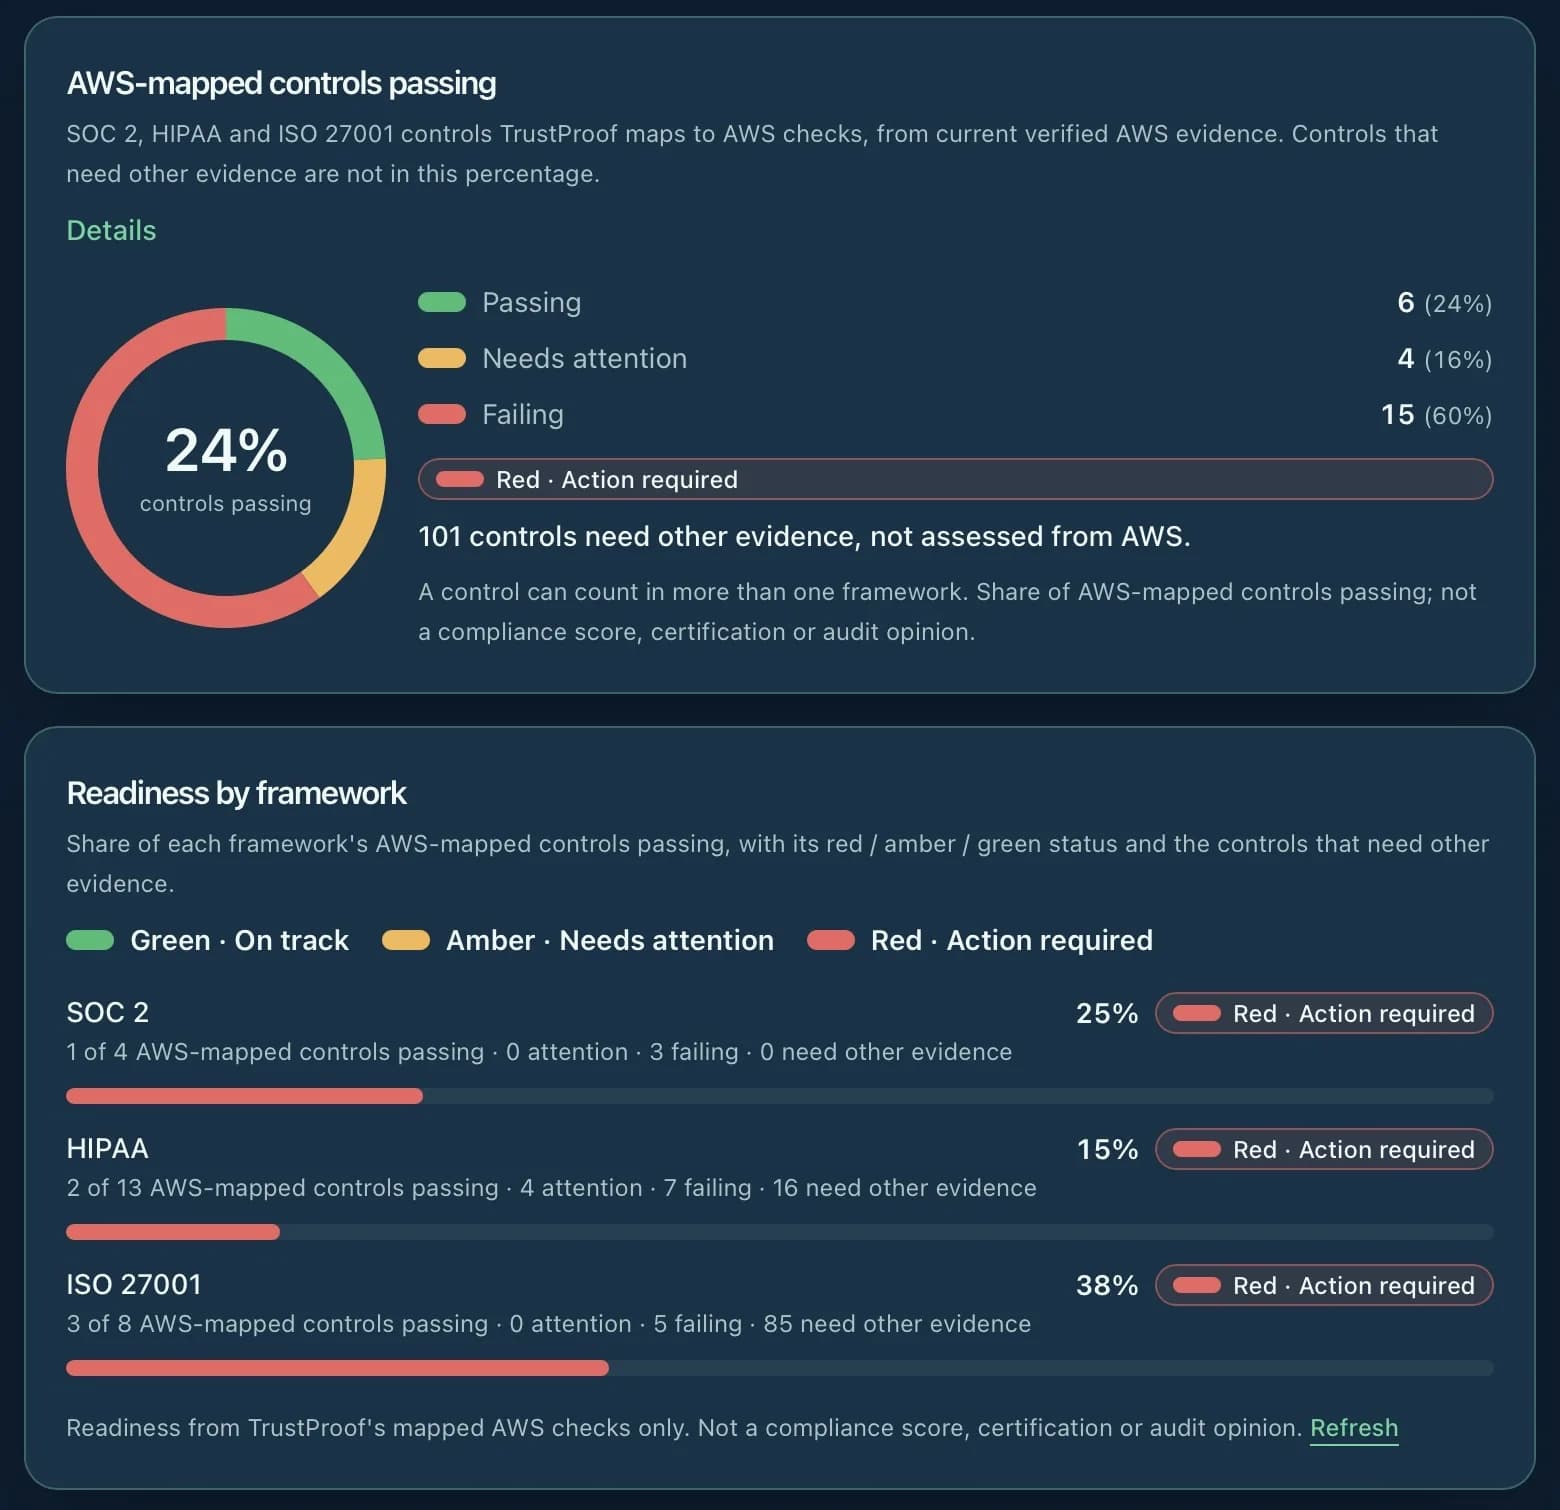
TrustProof scans your AWS account through a read-only role and maps the findings to ISO/IEC 27001:2022 Annex A controls, so you can see where your AWS environment stands before a certification audit. Your dashboard shows red, amber or green readiness for the mapped controls, and the CPA dashboard organises the evidence for your auditor; certification is decided by an accredited certification body.
Key facts
What you can check
- Read-only AWS role
- TrustProof connects through a read-only IAM role you create from our CloudFormation template and can remove at any time. No passwords, no stored keys.
- Annex A mappings
- 21 selected AWS check sources map to eight of the 93 Annex A controls in ISO/IEC 27001:2022 (A.8.2, A.8.3, A.8.5, A.8.9, A.8.15, A.8.16, A.8.20 and A.8.24). The other controls rely on your policies, records and sign-offs.
- Red, amber, green readiness
- Your dashboard shows a red, amber or green ISO/IEC 27001 status, worked out from your latest scan and the evidence collected for each mapped control.
- CPA dashboard
- The CPA dashboard lists each mapped Annex A control with its evidence, source, collection date and freshness, and shows evidence gaps, so your auditor can review it. Export it as PDF or CSV.
- SHA-256 evidence snapshots
- Each scan finding used as evidence is stored once as a snapshot with a SHA-256 fingerprint and its collection date, so any later change can be detected.
- Read-only access for your CPA or auditor
- Invite your CPA or auditor to your workspace as a read-only auditor. They must sign in with two-step verification before they can see any evidence.
- Hosted in AWS Sydney
- TrustProof runs on AWS in the Sydney region (ap-southeast-2), encrypted at rest and in transit.
Guided programme
Guided ISO/IEC 27001 readiness programme
Live: a guided ISO/IEC 27001 readiness programme for your whole information security management system (118 requirements: clauses 4 to 10 and all 93 Annex A controls), with 33 policy and procedure templates, owner sign-offs pinned to a SHA-256 fingerprint and a Statement of Applicability export.
What TrustProof does
- Scans your AWS account through a read-only role and ranks findings by risk
- Maps findings to ISO/IEC 27001:2022 Annex A controls and shows a red, amber or green readiness status
- Collects the evidence for each mapped control in a CPA dashboard, exportable as PDF or CSV
- Prepares fixes that your engineer approves before anything changes
What TrustProof doesn't do
- TrustProof does not certify. Certification is decided by an accredited certification body after its own audit.
- Its AWS checks map to eight Annex A controls; the rest needs your policies and records.
- It does not recreate your security posture from before you connected.
- It does not change your AWS account without an approval you give.
FAQ
Frequently asked questions
Does TrustProof certify us to ISO/IEC 27001?
No. Certification is decided by an accredited certification body (in Australia, usually one accredited by JAS-ANZ). TrustProof gets your AWS evidence ready and gives your auditor read-only access to it.
Which Annex A controls do the AWS checks cover?
21 selected AWS check sources map to eight of the 93 Annex A controls in ISO/IEC 27001:2022 (A.8.2, A.8.3, A.8.5, A.8.9, A.8.15, A.8.16, A.8.20 and A.8.24). The other 85 are not mapped by the current AWS checks.
Can TrustProof change my AWS account?
Not through the read-only connection. Fixes need a separate role that you add, and each fix runs only after your engineer approves it.
How does my auditor see the evidence?
Invite your auditor to your workspace as a read-only auditor. They sign in with two-step verification and see each mapped Annex A control with its evidence, source and collection date. You can also export it as PDF or CSV.
What does it cost?
The first AWS scan is free. One-Button Fix is A$1,499 one-off. Plans are a one-off Readiness Programme plus Continuous Monitoring from A$899 a month. All prices are in Australian dollars and include GST.