TrustProof / Capability boundaries
A clearer path from AWS signals to audit-ready preparation.
TrustProof is the Expert Coach. It collects selected evidence, detects selected policy drift and organises a reviewable trail. Your team approves and executes AWS changes; your independent CPA firm tests the evidence and issues its own SOC 2 report (an attestation, not a certification); for ISO standards, an accredited certification body decides on certification.
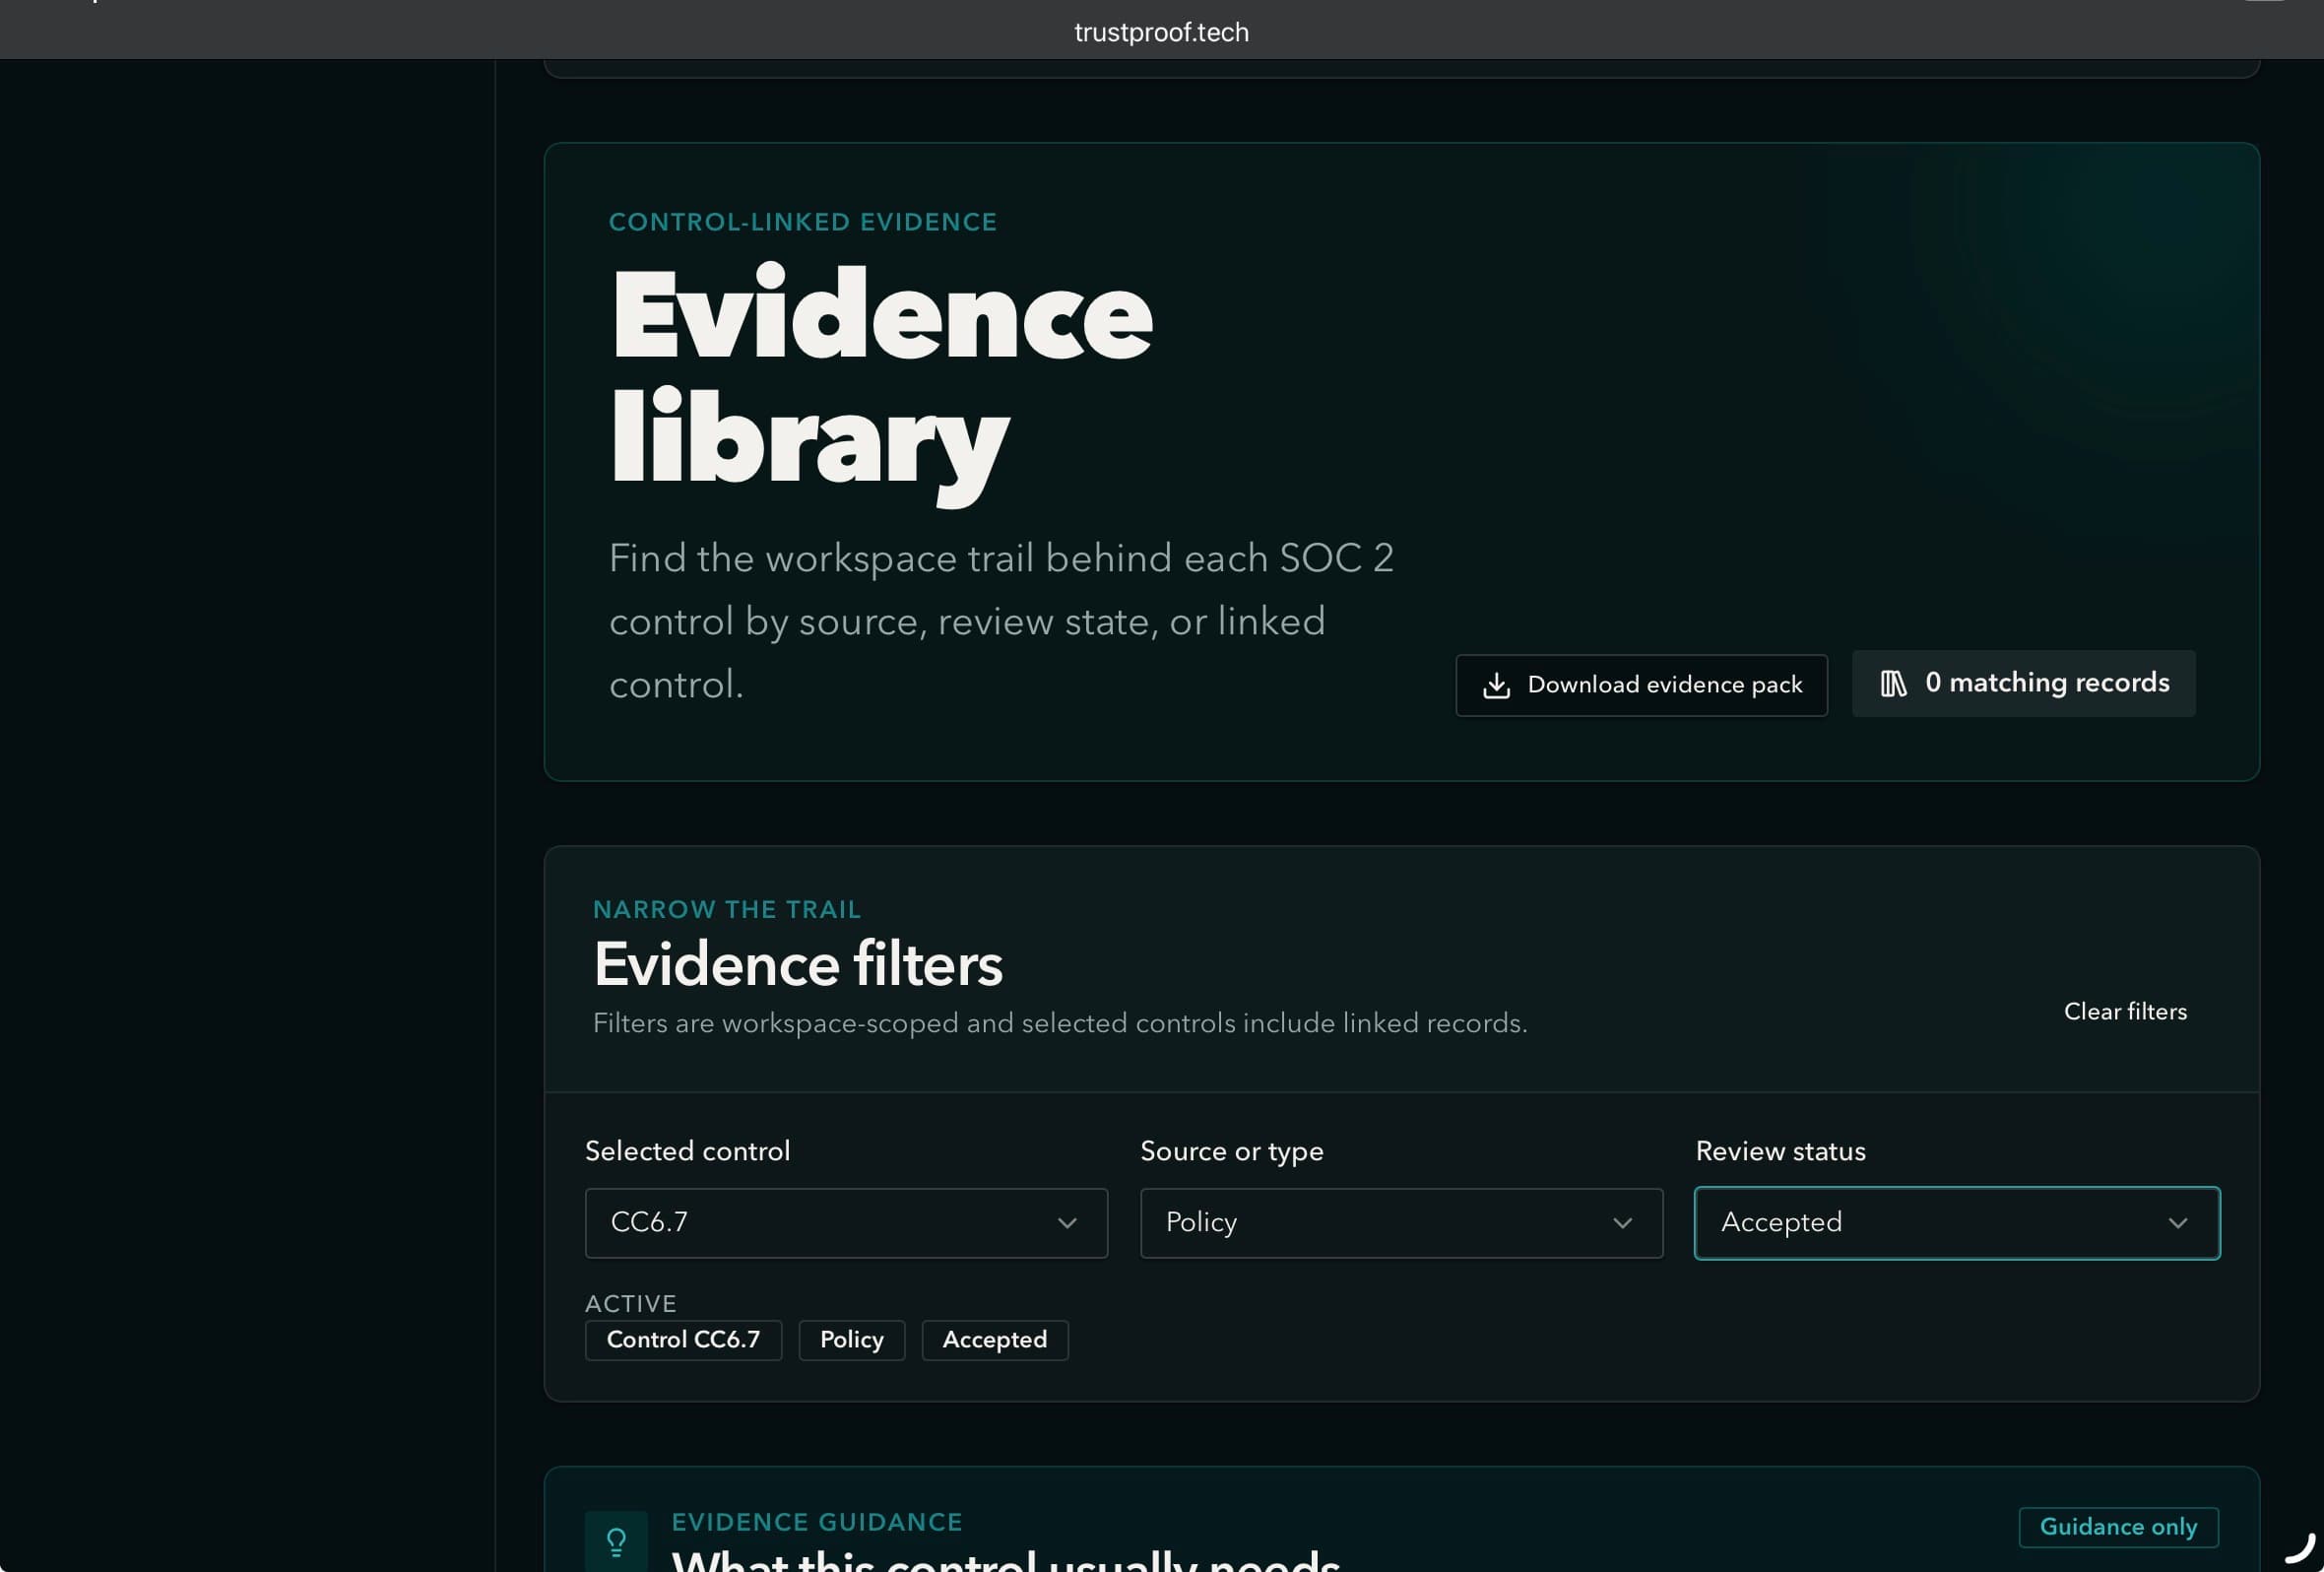
AWS evidence collection
Build the trail from the connection date forward.
TrustProof uses read-only access to gather supported AWS evidence after a verified connection. That gives teams a dated starting point for preparation; it does not recreate pre-connection posture or provide retroactive proof.
The evidence trail is context for readiness work, not a statement that every audit requirement or control is covered.
Policy drift detection
Detect the signals that deserve a closer look.
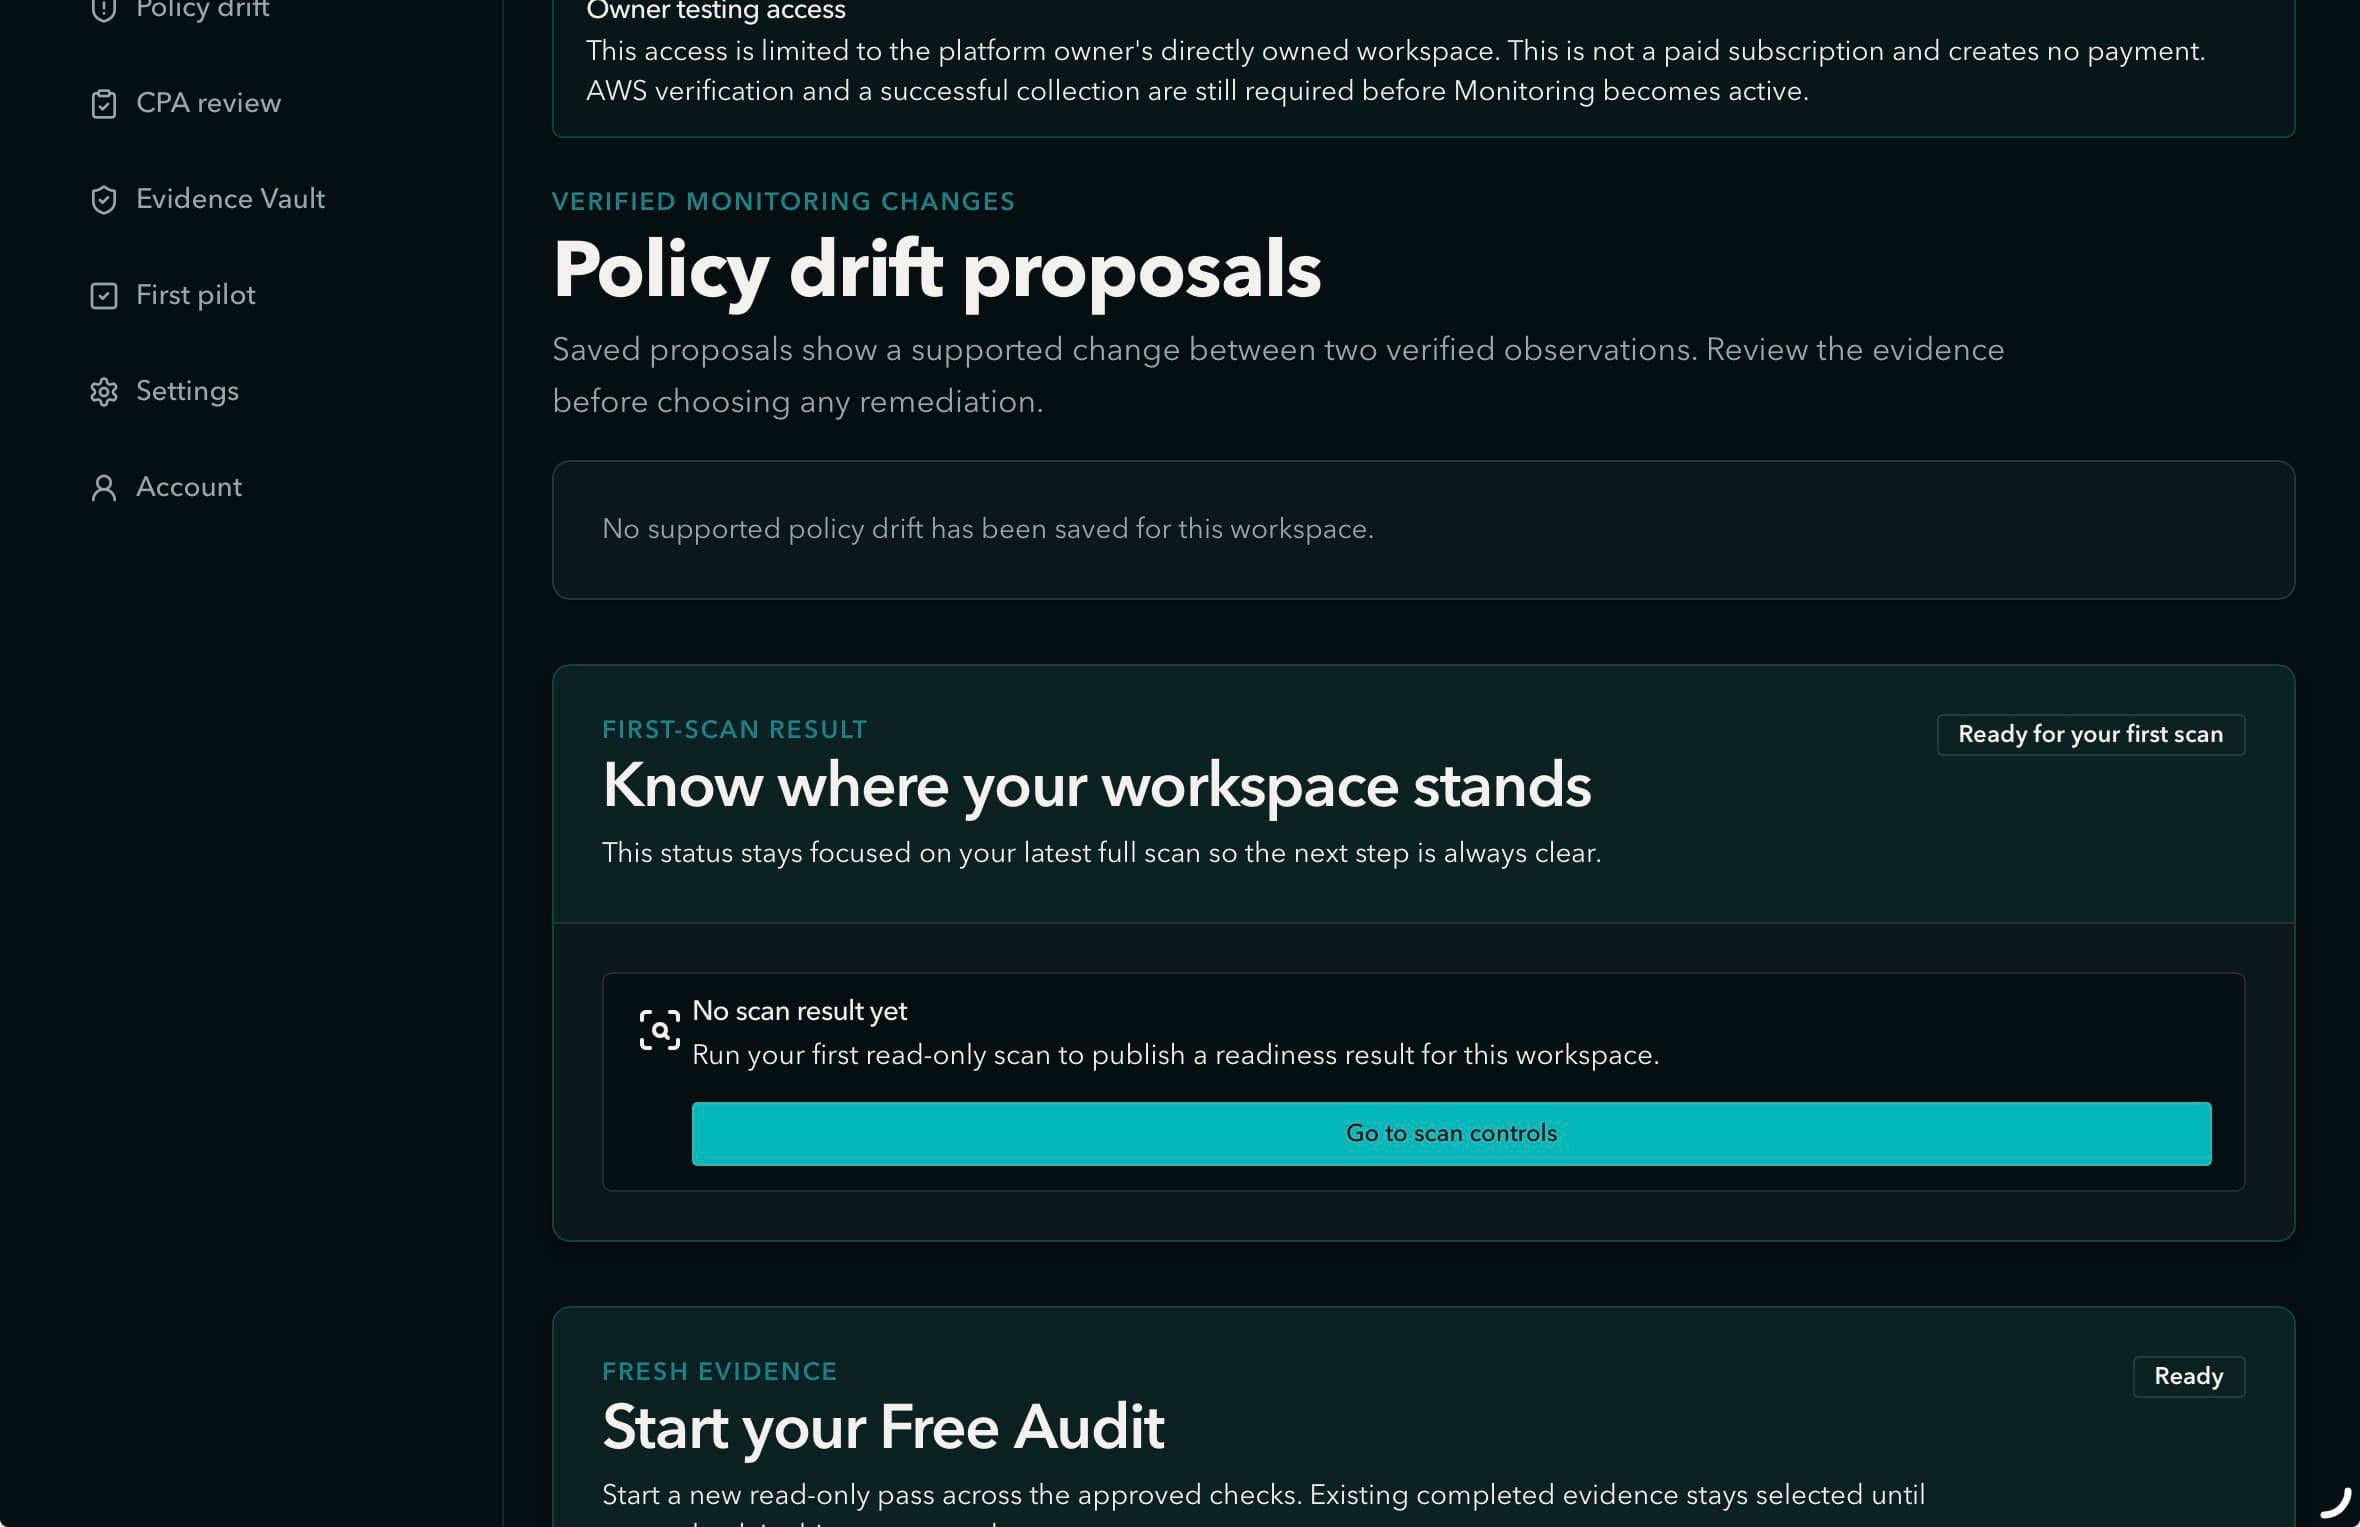
The current AWS checks cover a defined set of high-impact observations. TrustProof surfaces them for investigation and review; it does not make the AWS change for you.
Proposal and review
A finding becomes a decision, not an unapproved action.
Supported findings can become reviewable proposals. The customer decides whether to approve the proposed next step, executes the AWS fix in its own environment and can then verify the resulting evidence. A proposal review is not proof that the change was executed.
TrustProof detects and guides.
The customer reviews, approves and executes.
Evidence records what is available after the customer's work.
Evidence mapping and CPA Dashboard
Organised context for the independent CPA.
Supported evidence is pre-mapped to the current control references in the CPA Dashboard so a reviewer can see the source, context and follow-up state together. This is not complete framework coverage and it is not certification.
Selected AWS checks are mapped to 13 HIPAA Security Rule references, eight ISO/IEC 27001:2022 Annex A controls, and limited SOC 2 traceability for CC6.1, CC6.6, CC6.7 and CC7.2.
Open the CPA Dashboard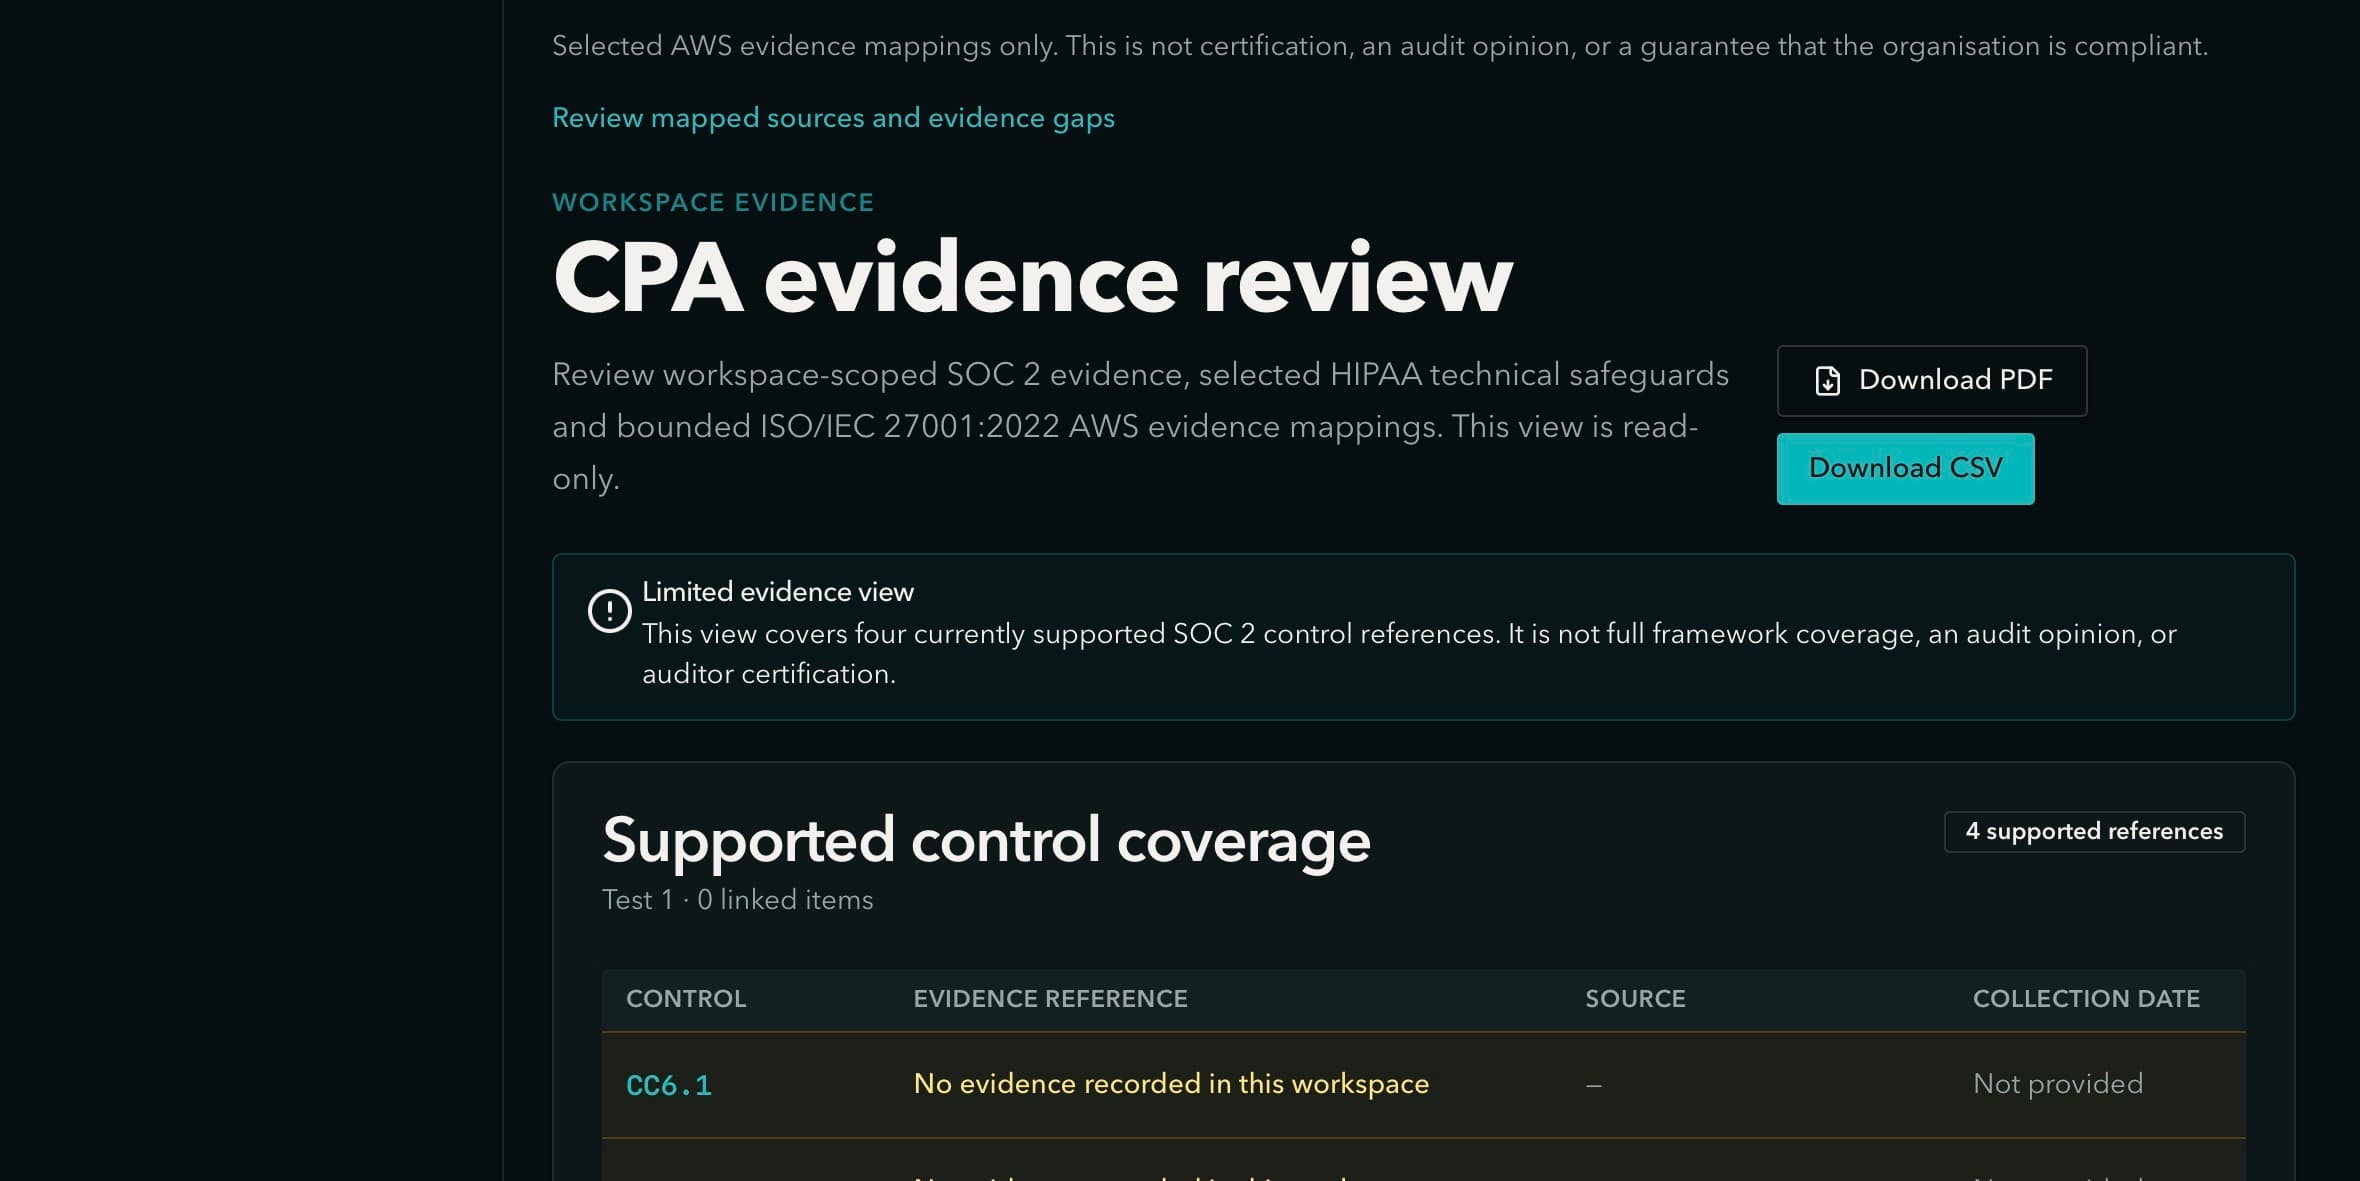
Readiness Baseline
Two tracks. One preparation habit.
Build it right the first time with Compliance-as-Code habits, enterprise readiness and an earlier evidence trail. Or fix it, monitor it, prove it with detection, investigation, guided customer-executed changes and evidence organisation.
Initial scan
Review supported AWS observations from the configured read-only connection.
Gap analysis
Separate available evidence, follow-up questions and unsupported areas.
Guided roadmap
Propose a next step for customer approval and execution in the AWS environment.
Preparation you can explain.
The Readiness Baseline gives your team an initial scan, gap analysis and guided roadmap without hiding the boundaries of what is currently supported.
Talk through your baseline